
The FedHIVE Story:
Innovation shouldn’t be delayed by compliance.
We helped pioneer the accelerator model. Now we’re evolving it for what comes next.
FedHIVE was born from firsthand experience with the cost, complexity, and uncertainty of bringing technology into government. We watched companies lose years, millions of dollars, and valuable engineering capacity navigating compliance instead of delivering innovation.
The hardest part wasn’t building secure technology. It was proving it – and operating it – in a way the government could continuously trust.
That insight became the foundation for FedHIVE.

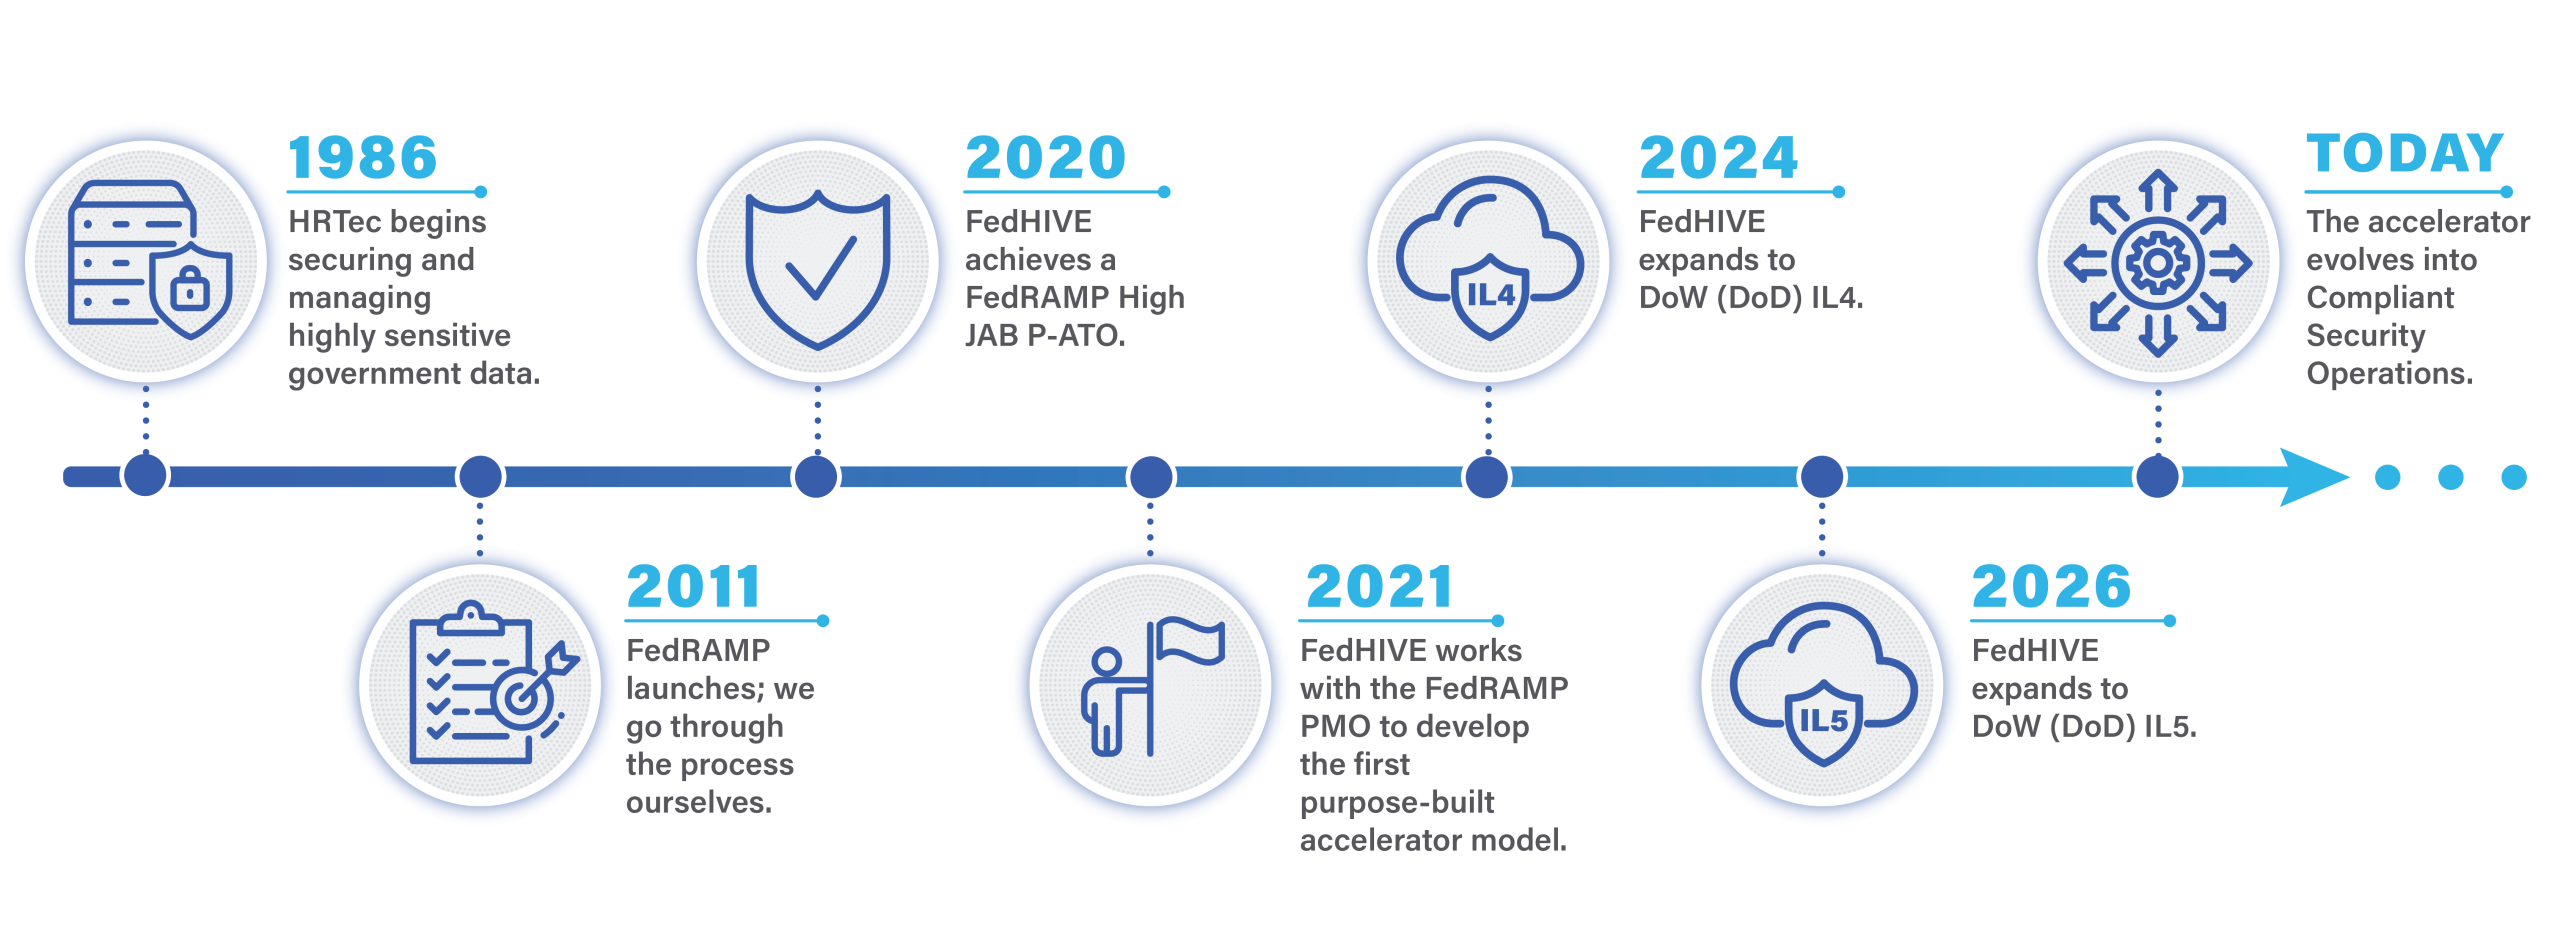
Four decades of securing government data—evolving from FedRAMP High and DoD authorization to Compliant Security Operations.
A Different Model
Working closely with the FedRAMP PMO, we developed a different path: combine a secure, authorized environment with the compliant security operations required to sustain it. Together, we established what could be consistently operated and reused within the FedHIVE boundary, and what still required customer-specific review.
Same rigorous standards. A completely reimagined architecture.
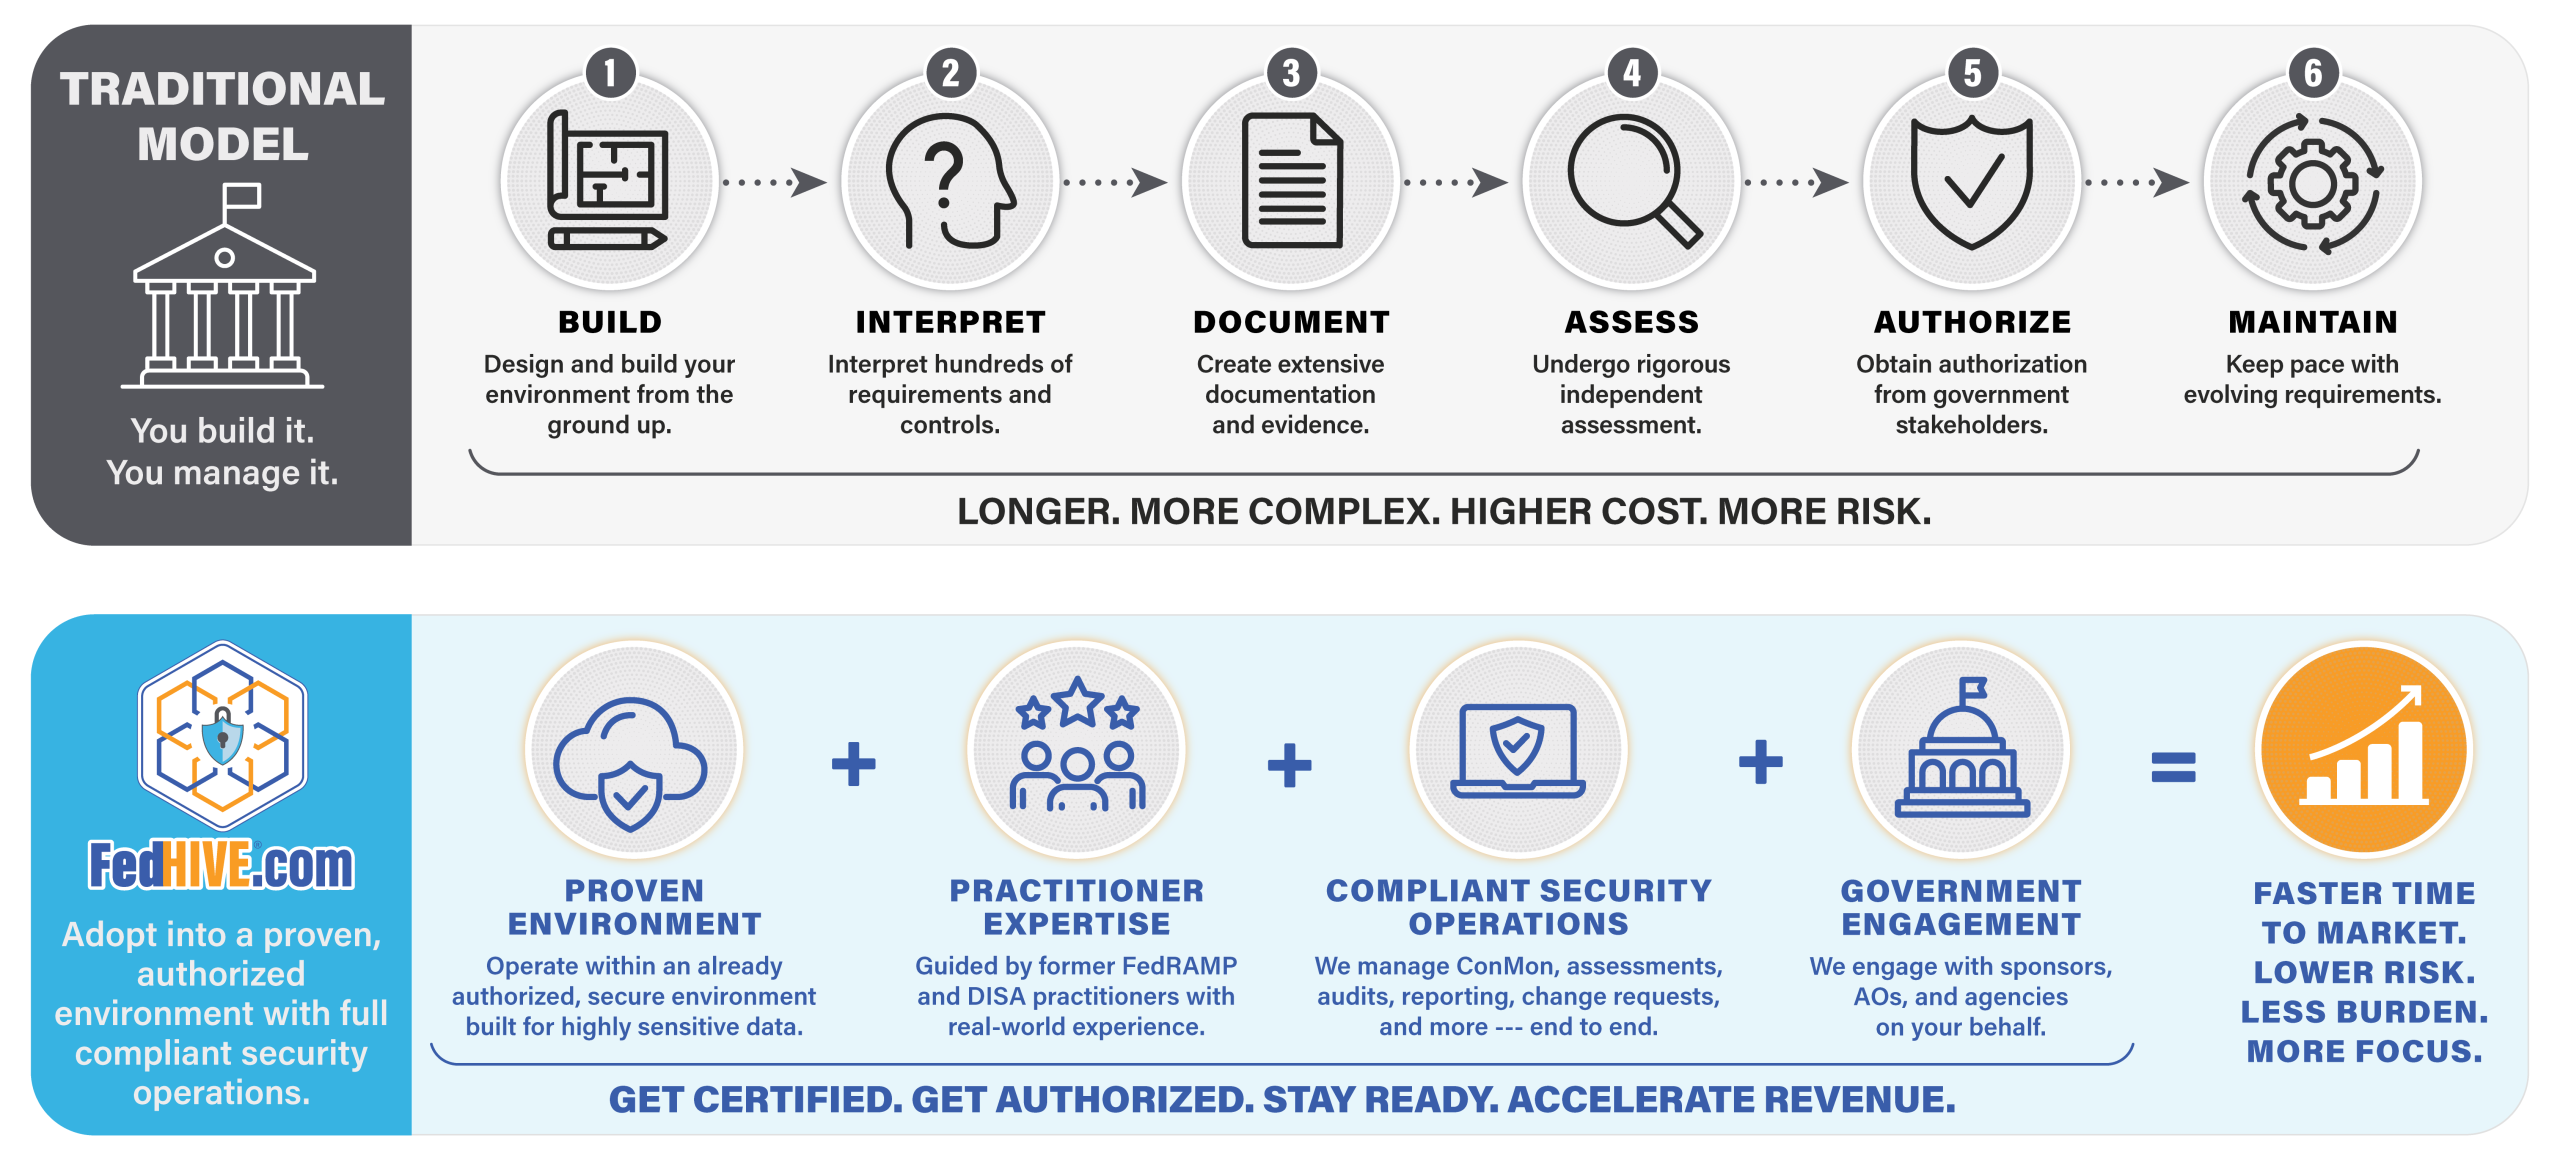
A different approach to federal cloud compliance—combining a proven environment, practitioner expertise, continuous compliant operations, and government engagement.
Why FedHIVE?
“HIVE” means High Impact Virtual Environment, but it also reflects how we believe government technology succeeds: through a coordinated ecosystem.
Government
Technology Companies
Secure Cloud (Public)
Secure Cloud (Private)
Assessors
Compliance Practitioners
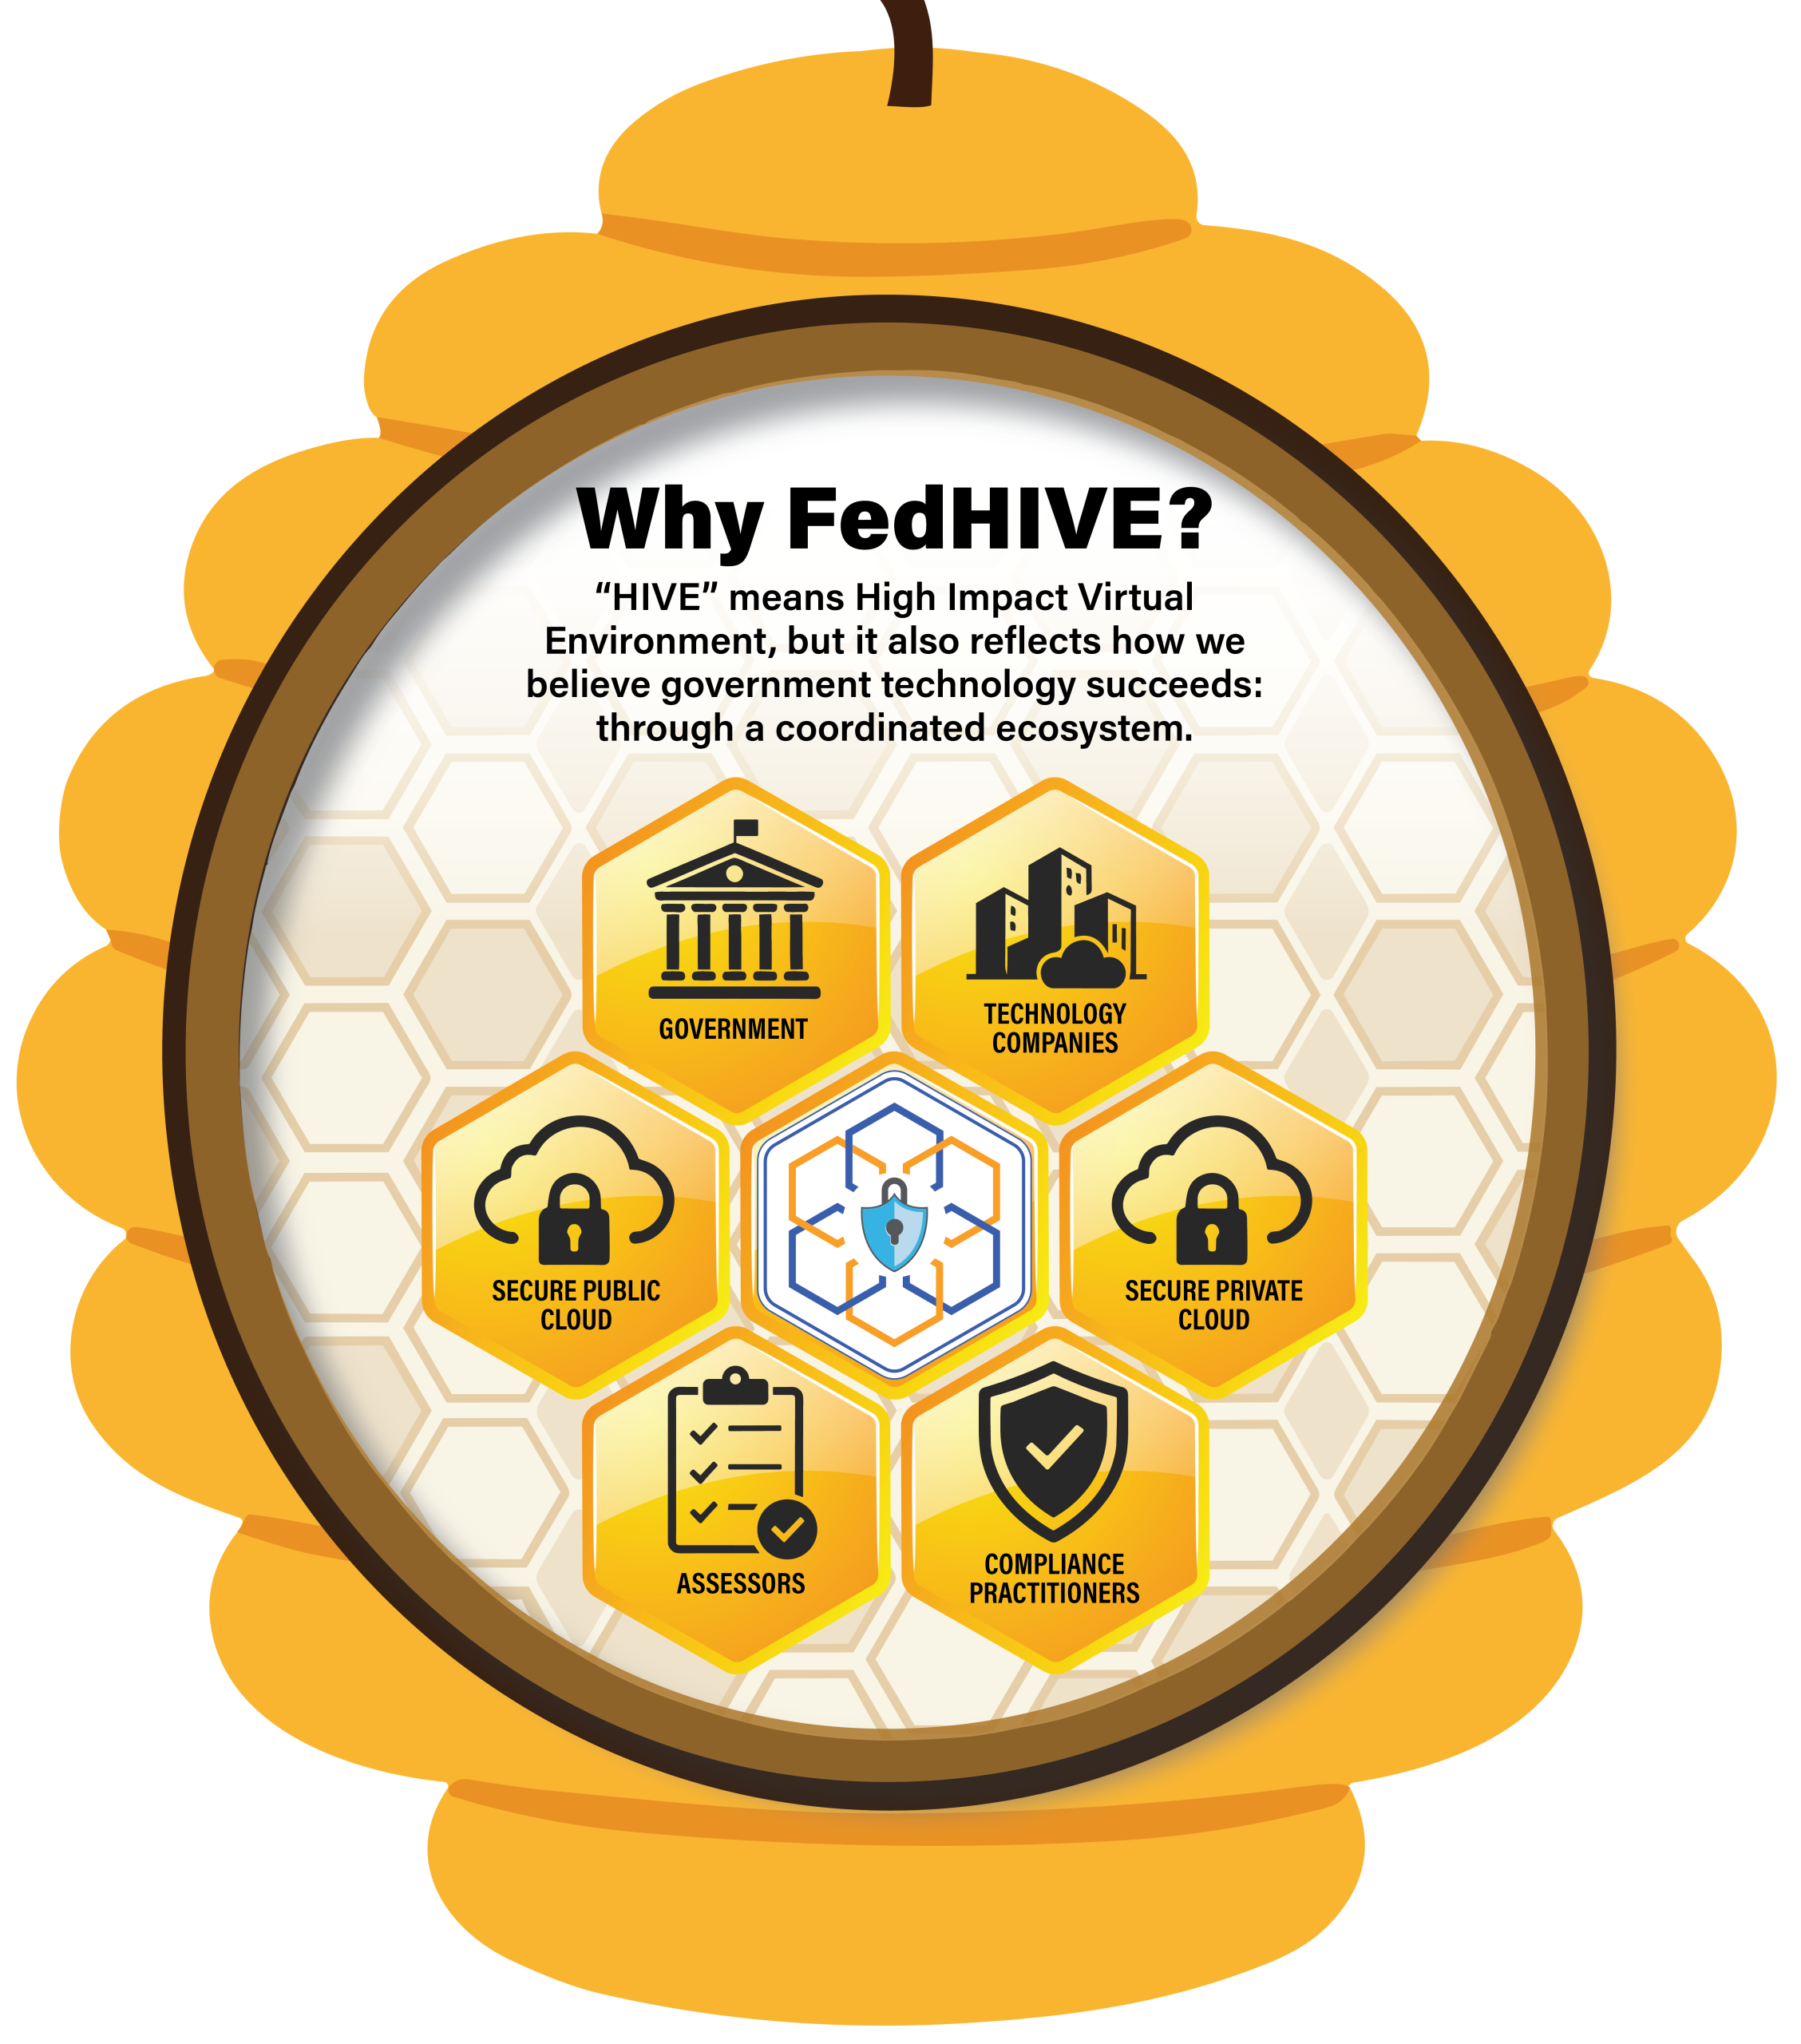
A continuous ecosystem of technology, compliance, partnership, and trust.
A Milestone That Validated the Model
FedHIVE became the first small business – and the first and only small-business IaaS/PaaS/SaaS cloud service offering – to achieve it.
FedRAMP has since evolved beyond the JAB authorization model, but the operating discipline established through that process remains foundational today.
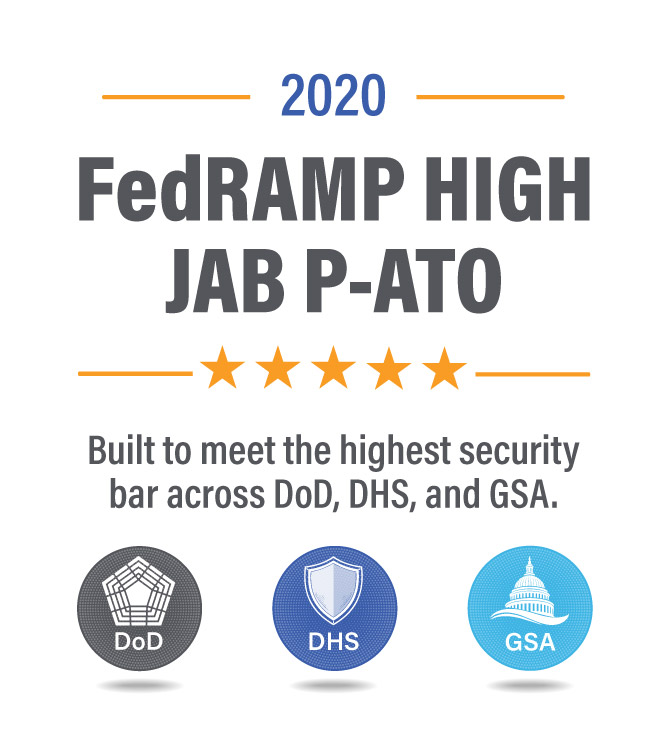
Built to meet the highest common security bar across DoD, DHS, and GSA.
From Accelerator to Compliant Security Operations
The accelerator solved an important problem: helping technology companies reach compliance without building everything from scratch. But the market has changed.
Compliance now reaches deeper into product architecture, integrations, development, security operations, assessments, government engagement, and growth. Companies must reach the first milestone – then stay ready for the products, agencies, environments, and requirements that come next.
That is why FedHIVE is evolving the accelerator into Compliant Security Operations: an ongoing discipline that brings secure infrastructure, practitioner expertise, compliance operations, and government engagement together throughout the lifecycle.
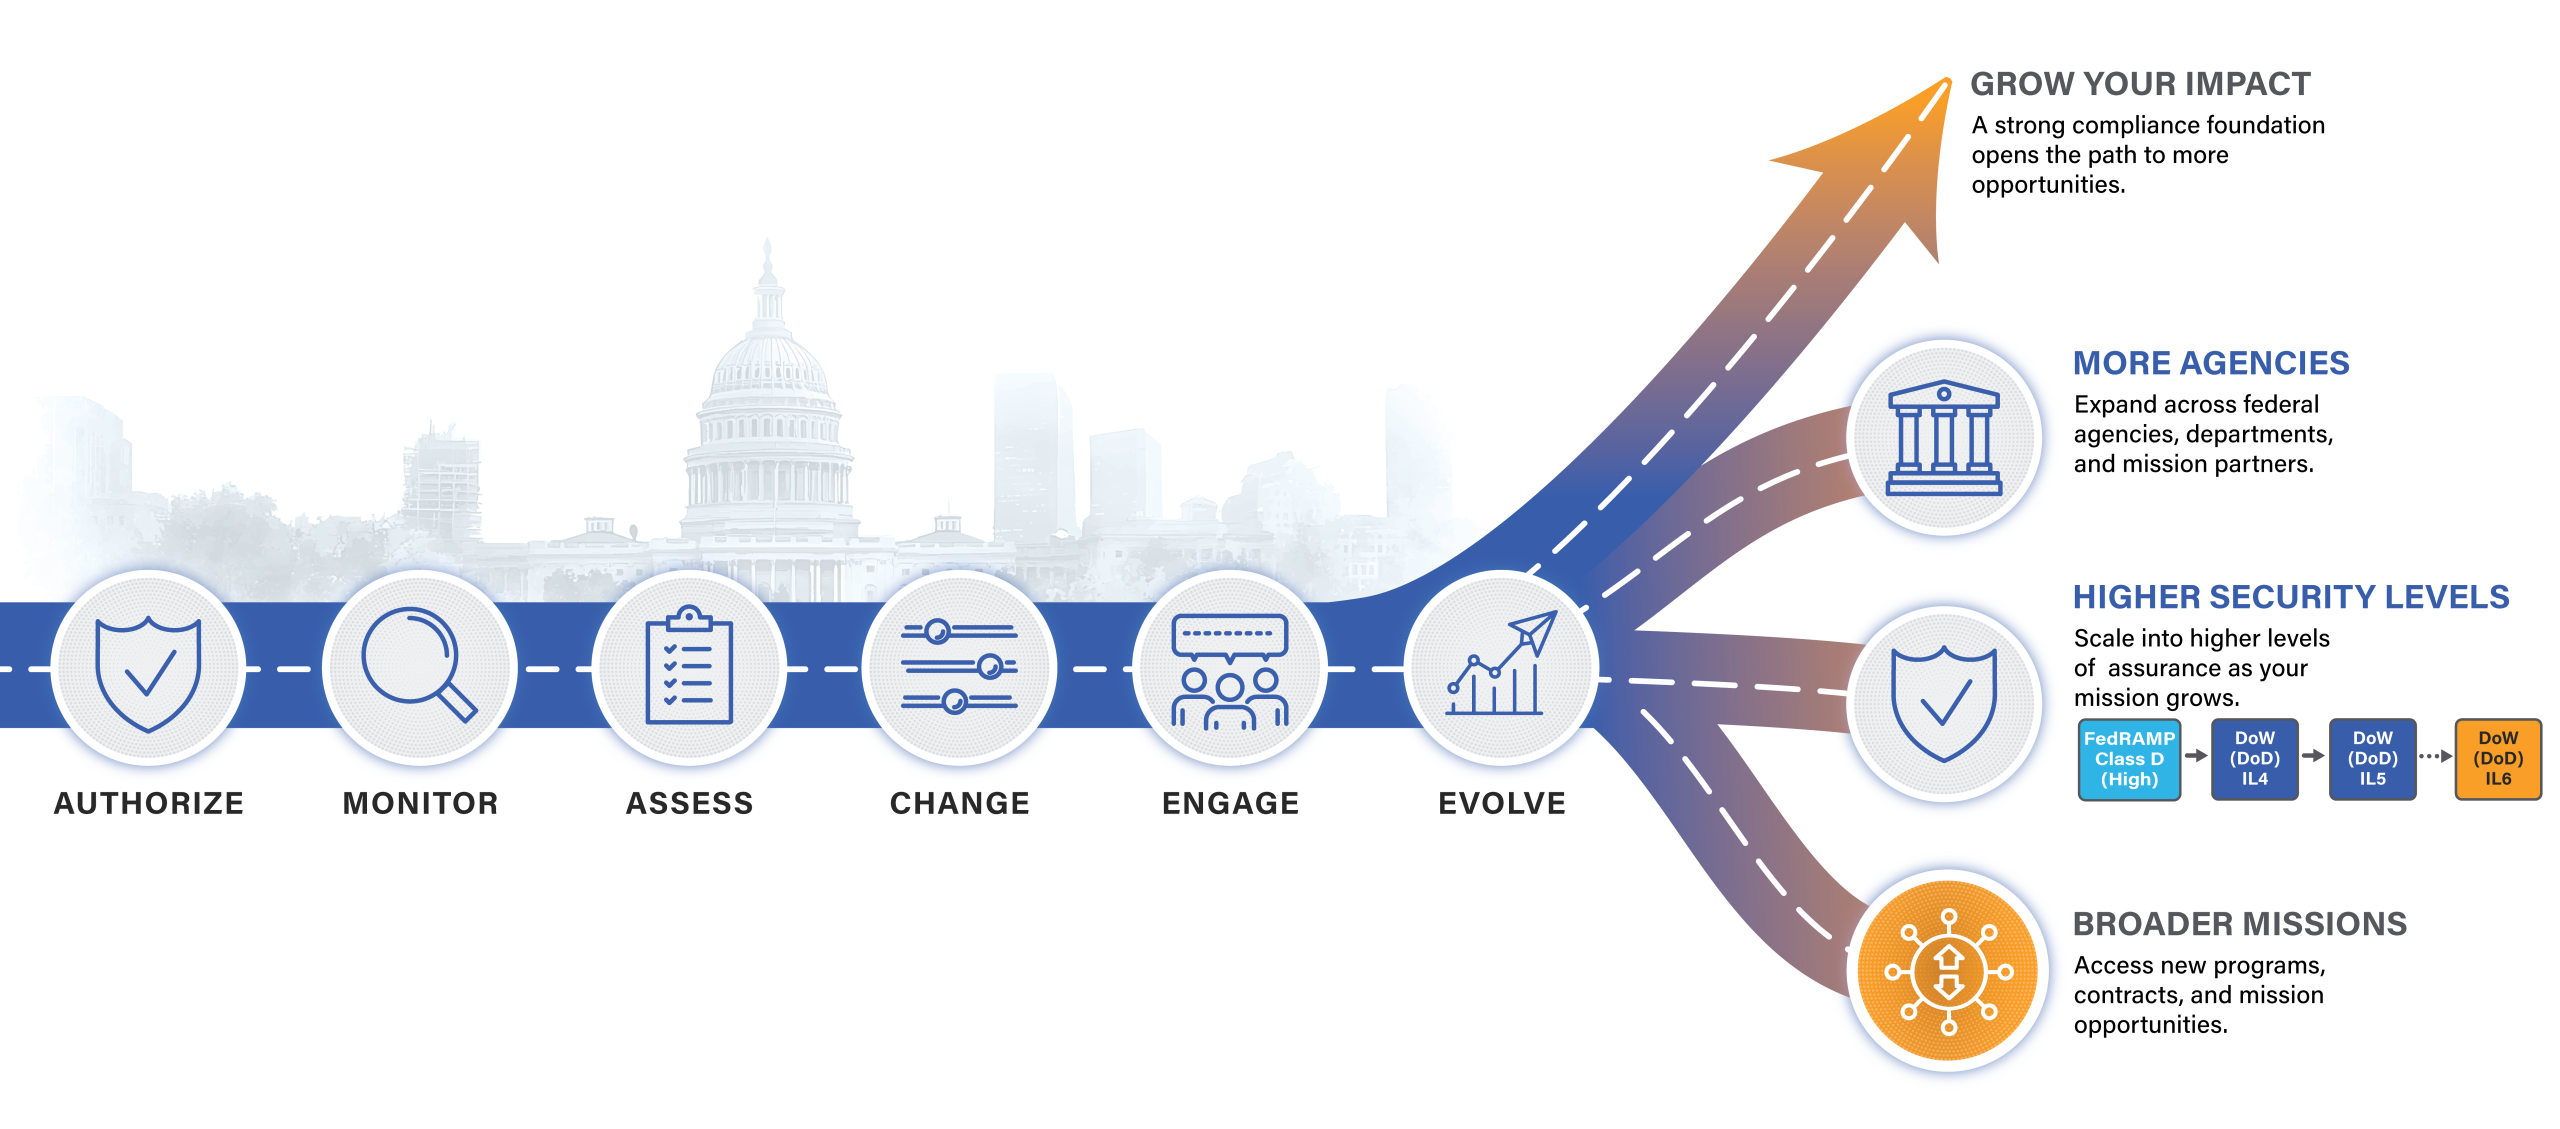
Continuous compliance creates a foundation for growth—supporting higher security levels, more government agencies, and broader mission opportunities.
Built for Complexity. Designed for Growth.
FedHIVE supports complex architectures, sophisticated data flows, regulated workloads, multiple clouds, integrations, highly sensitive data, and mission-critical applications – without forcing customers into a predetermined deployment model.
That flexibility is backed by nearly four decades of government technology experience and former working-level FedRAMP and DISA practitioners who have performed assessments, authorization packages, continuous monitoring, and compliance operations.
We don’t just interpret requirements. We understand how to put them into practice and sustain them as products and government businesses grow.
Built for What Comes Next
Our mission is to make the government market more accessible for innovative technology companies.
Organizations should succeed because they build exceptional technology, not because they can afford to spend years and millions navigating compliance complexity.
By providing a faster, more predictable, and more cost-effective path to operating at the highest levels of security, we help customers bring transformative technologies to government sooner – without compromising the security those missions demand.
Ready to Accelerate Your Federal Growth?
Whether you're pursuing FedRAMP Class D (High), DoW (DoD) IL4/IL5, GovRAMP, CMMC, or looking to reduce the operational burden of maintaining an existing authorization, FedHIVE provides the trusted foundation, practitioner expertise, and managed compliance operations to help you grow with confidence.
